Microsoft Defender for Endpoint
Microsoft Defender for Endpoint is an AI-powered endpoint security platform that helps businesses prevent, detect, and respond to cyber threats across devices like laptops, servers, and mobile systems. It combines antivirus, threat intelligence, and automated response to stop attacks, reduce risk, and provide full visibility across environments.
What is Microsoft Defender for Endpoint?
Microsoft Defender for Endpoint is a cloud-native, AI-powered endpoint security platform that helps organizations prevent, detect, investigate, and respond to cyber threats across devices like Windows, macOS, Linux, Android, iOS, and IoT systems. It provides capabilities such as endpoint detection and response (EDR), vulnerability management, attack surface reduction, and automated threat remediation, all managed from a single dashboard. By combining real-time monitoring with global threat intelligence and AI-driven insights, it helps businesses identify risks early, stop attacks like ransomware, and maintain strong, centralized security across their entire environment.
Positioned as a continuous Leader in the Gartner Magic Quadrant for Endpoint Protection Platforms (EPP) and ranking among the top detection performers across MITRE ATT&CK Enterprise Evaluations, Microsoft Defender for Endpoint protects tens of millions of enterprise devices globally. Backed by Microsoft's daily analysis of over 78 trillion cyber threat signals, Defender for Endpoint combines behavioral heuristics with cloud-delivered AI intelligence. By correlating cross-domain endpoint alerts directly with identities, email, and cloud SaaS in the unified Microsoft Defender portal, it empowers security teams to investigate and remediate complex attacks at machine speed.
- Developer / Parent Company: Microsoft Corporation (Redmond, WA)
- Launch Year: 2016 (Originally Windows Defender ATP; evolved into Microsoft Defender for Endpoint)
Use Cases:
- Blocking fileless malware, credential dumping, zero-day exploits, and ransomware via hardware-backed attack surface reduction (ASR) rules
- Automating deep root-cause investigations and executing autonomous machine containment using Automated Investigation and Remediation (AIR)
- Managing organizational attack surface vulnerabilities and software patch priorities with Defender Vulnerability Management
- Running advanced Kusto Query Language (KQL) threat-hunting queries and accelerating SecOps investigations via Microsoft Security Copilot
Technology:
- Agentless kernel-level OS instrumentation on Windows, paired with lightweight enterprise daemons for macOS, Linux, and mobile
- Global Microsoft Threat Intelligence graph synthesizing multi-trillion signal daily telemetry across endpoints, identities, and clouds
- Kusto Query Language (KQL) hunting engine powering custom detection rules and unified incident correlation graphs
Target Users:
- Enterprise CISOs and SOC managers looking to consolidate third-party security agents and maximize Microsoft 365 E5 ROI
- Windows and hybrid sysadmins managing thousands of corporate endpoints using Microsoft Intune and Group Policy
- Threat hunters and Tier 2-3 SOC analysts executing custom detection playbooks and incident response investigations
- Content creators using writing tools to draft incident response playbooks, internal patch management memos, and corporate security guidelines
Corporate Entity: Operates as Microsoft Corporation (NASDAQ: MSFT, Redmond, WA & Global)
Key features of Microsoft Defender for Endpoint
Microsoft Defender for Endpoint's key features are
- Native OS Integration: Embedded directly into Windows 10 and 11, eliminating the stability risks, high RAM overhead, and conflicts associated with installing third-party kernel drivers.
- Behavioral EDR & Process Trees: Real-time behavioral monitoring and post-breach detection that maps attacker techniques directly to the MITRE ATT&CK framework with visual execution trees.
- Automated Investigation & Remediation (AIR): Employs AI inspection playbooks to autonomously investigate suspicious artifacts, terminate malicious processes, remove registry run keys, and isolate compromised hosts 24/7.
- Attack Surface Reduction (ASR) Rules: Hardens system postures against common entry vectors, preventing executable content from email clients, malicious Office macros, and credential theft from LSASS.
- Defender Vulnerability Management: Continuously inventories installed software, discovers unpatched vulnerabilities (CVEs), and assigns risk scores prioritized by active exploit telemetry.
- Advanced Hunting with KQL: Search through up to 30 days of raw endpoint telemetry using Kusto Query Language (KQL) to construct custom threat detections and forensic queries.
- Microsoft Security Copilot: Generative AI natural-language assistant embedded directly in the Defender portal to summarize incidents, interpret complex scripts, and guide containment steps.
- Cross-Platform Support: Unified administration, EDR, and vulnerability assessment across Windows, Windows Server, macOS, Linux distributions, iOS, and Android.
Microsoft Defender for Endpoint Pricing
Microsoft Defender for Endpoint is available as a standalone per-user subscription (covering up to 5 devices per licensed user) or bundled into broader enterprise Microsoft 365 licensing suites.
Standalone Monthly Plans:
- Defender for Endpoint Plan 1 (P1): $3.00 per user/month (Includes next-gen antimalware, Attack Surface Reduction, device control, and manual response actions)
- Defender for Endpoint Plan 2 (P2): $5.20 per user/month (Adds full behavioral EDR, Automated Investigation and Remediation [AIR], threat vulnerability management, sandboxing, and advanced KQL hunting)
- Defender for Business: $3.00 per user/month (Tailored standalone plan for SMBs with up to 300 users; also included in Microsoft 365 Business Premium)
Enterprise Licensing Bundles:
- Included in Microsoft 365 E5, A5, and G5 enterprise suites (Full Plan 2 included alongside Defender for Identity, Office 365 P2, and Cloud Apps)
- Microsoft Defender Suite (E5 Security Add-on for M365 E3): $12.00 per user/month (or ~₹1,000/user/month in India)
- Defender for Servers (Cloud Workload Protection): Billed usage-based via Microsoft Defender for Cloud at ~$5/server/month (Plan 1) or ~$15/server/month (Plan 2)
Disclaimer: Standalone licenses allow each user to onboard up to 5 concurrent client devices. Server endpoints require separate licensing via Defender for Servers. For regional currency rates, volume licensing, and enterprise agreement terms, visit microsoft.com/en-in/security/microsoft-defender-pricing.
Who is using Microsoft Defender for Endpoint?
Microsoft Defender for Endpoint is designed for IT and security professionals across organizations of all sizes, including
- Enterprise Corporations & Global Conglomerates: Securing enterprise workforces across hundreds of thousands of distributed Windows, Mac, and Linux machines
- Microsoft 365 E5 & E3 Enterprise Customers: Maximizing cybersecurity ROI by replacing disparate third-party EDR tools with native Microsoft security
- State, Local & Education (SLED) Organizations: Defending school districts, universities, and municipal services under Microsoft A5 educational agreements
- Financial & Healthcare Institutions: Meeting strict compliance mandates (HIPAA, PCI-DSS, SOC 2) with automated vulnerability patching and continuous auditing
- Content Creators: Using writing tools to draft incident response playbooks, internal patch management memos, and corporate security guidelines
- Small & Medium Businesses (SMBs): Protecting up to 300 devices with zero configuration overhead via Defender for Business
Best Microsoft Defender for Endpoint Alternatives
Some of the strongest Microsoft Defender for Endpoint alternatives include
- CrowdStrike Falcon
- SentinelOne
- Huntress
- Sophos Intercept X
- Palo Alto Networks Cortex XDR
- Trend Micro Vision One
Pros and Cons of Microsoft Defender for Endpoint
Pros
- Built natively into Windows OS, eliminating third-party agent installation overhead, kernel instability, and update reboots
- Exceptional value for organizations already subscribed to Microsoft 365 E5 or E3 with the E5 Security add-on
- Deep cross-domain XDR integration linking endpoint signals with Entra ID, Defender for Office 365, and Cloud Apps
- Automated Investigation and Remediation (AIR) autonomously resolves threats, significantly decreasing SOC alert fatigue
- Backed by the unmatched global scale of Microsoft Threat Intelligence, processing 78+ trillion signals daily
Cons
- Advanced hunting, full behavioral EDR, and automated remediation require Plan 2 ($5.20/user/mo) or E5 licensing
- Managing policies across non-Windows operating systems (macOS, Linux) requires third-party MDM or Microsoft Intune configuration
- The unified Defender security portal features deep configuration trees that can present a steep learning curve for junior sysadmins
- Server endpoints must be licensed and monitored separately through Azure Arc and Defender for Servers
Why Choose Microsoft Defender for Endpoint?
Microsoft Defender for Endpoint is the premier choice for organizations that want enterprise-grade endpoint security and XDR woven directly into the fabric of their operating system.
- Eliminates agent bloat with seamless, native Windows deployment and centralized Intune management
- Reduces licensing costs dramatically by consolidating multiple security tools into your Microsoft 365 agreement
- Unifies endpoint telemetry with identity, email, and cloud applications in a single incident queue
- Accelerates incident response through autonomous AI remediation and Microsoft Security Copilot
- Validated by Gartner, MITRE, and enterprise security leaders as an industry benchmark for endpoint defense
Microsoft Defender for Endpoint vs. Competitors
The main difference between Microsoft Defender for Endpoint, CrowdStrike Falcon, SentinelOne, and Huntress is that Microsoft Defender is natively integrated into Windows operating systems and tightly coupled to the broader Microsoft 365 security ecosystem at $3.00 to $5.20/user/month, whereas CrowdStrike Falcon relies on proprietary Threat Graph adversary intelligence and a single cross-platform cloud sensor, SentinelOne focuses on on-agent autonomous behavioral AI with ransomware rollback, and Huntress provides an SMB/MSP-focused platform bundling a 24/7 human SOC. Microsoft Defender stands out for its cost-effective enterprise bundling, agentless Windows deployment, and native XDR correlation.
| Feature / Tool | Microsoft Defender for Endpoint | CrowdStrike Falcon | SentinelOne Singularity | Huntress |
|---|---|---|---|---|
| Core Focus | Native Windows & M365 Ecosystem EDR | Adversary Intelligence & Cloud EDR | Autonomous On-Agent Behavioral XDR | Managed EDR & 24/7 SOC for SMB/MSP |
| Deployment Type | Built-in to Windows (Agentless client) | Single Lightweight Cloud Sensor | Single Autonomous Host Agent | Lightweight Host Agent + Cloud |
| Automated Remediation | AIR (Automated Investigation & Fix) | Falcon Real Time / Custom Scripts | 1-Click Ransomware Rollback | Assisted 1-Click Remediation |
| AI Copilot Integration | Microsoft Security Copilot | Charlotte AI & AgentWorks | Purple AI Copilot | SOC Investigation Automation |
| Starting Paid Price | $3.00 (P1) / $5.20 (P2) / In M365 E5 | $59.99/device/year (Falcon Go) | ~$35.00–$70.00/endpoint/year | Custom Flat SMB/MSP Rates |
| Best For | Organizations with Microsoft 365 Stacks | Mission-Critical Enterprise Breaches | Autonomous On-Device Remediation | SMBs, MSPs & Lean Corporate Teams |
How do we rate Microsoft Defender for Endpoint?
| Parameter | Rating (out of 5) |
|---|---|
| Threat Detection & Behavioral EDR Quality | 4.9 |
| Native Windows OS Ergonomics & Deployment | 5.0 |
| Automated Investigation & Remediation (AIR) | 4.9 |
| Unified M365 Security & XDR Ecosystem | 5.0 |
| Value for Money | 4.9 |
| Overall Score | 4.94 |
Microsoft Defender for Endpoint Review
Microsoft Defender for Endpoint represents one of the most successful product evolutions in the history of cybersecurity. What began years ago as basic consumer Windows antivirus has matured into a tier-1 enterprise detection and response powerhouse that consistently ranks among the top performers in independent third-party evaluations. Its biggest competitive advantage is its native presence inside Windows: because the underlying detection hooks are built into the operating system itself, organizations eliminate the kernel crashes, stability hazards, and software update headaches that often plague third-party agents. When combined with Automated Investigation and Remediation (AIR), KQL advanced hunting, and seamless integration across Entra ID and Office 365, Defender for Endpoint delivers unbeatable security ROI for Microsoft-centric organizations.
Conclusion
Microsoft Defender for Endpoint is an industry-standard enterprise endpoint security and XDR platform that redefines how organizations protect workstations, servers, and mobile devices. By combining native Windows OS integration, behavioral EDR, automated investigation and remediation, vulnerability management, and Microsoft Security Copilot into an integrated cloud portal, it provides deep defense without endpoint bloat. While non-Windows fleet management requires Intune or third-party MDM, Defender for Endpoint’s detection excellence, global threat intelligence, and unmatched Microsoft 365 value make it an indispensable security platform.
FAQ
What is Microsoft Defender for Endpoint and how does it work?
Microsoft Defender for Endpoint is a cloud-native, AI-powered endpoint security platform that helps organizations prevent, detect, investigate, and respond to cyber threats across devices. It works by deploying a lightweight agent on endpoints such as Windows, macOS, Linux, Android, and iOS, which continuously collects signals and sends them to Microsoft’s cloud. These signals are analyzed using AI and global threat intelligence to identify attacks and automatically respond to them in real time.
What problems does Microsoft Defender for Endpoint solve?
Microsoft Defender for Endpoint helps organizations tackle modern cybersecurity challenges like ransomware, zero-day exploits, and identity-based attacks. Many traditional tools fail to detect sophisticated threats or require manual intervention, but Defender provides automated detection, investigation, and remediation, enabling faster response and reducing the risk of breaches across complex IT environments.
What features does Microsoft Defender for Endpoint offer?
Microsoft Defender for Endpoint offers a comprehensive set of capabilities including endpoint protection, endpoint detection and response (EDR), vulnerability management, attack surface reduction, and automated investigation and remediation. It also provides advanced threat hunting, network detection, and integration with Microsoft Defender XDR for unified visibility across devices, identities, and cloud workloads.
How is Microsoft Defender for Endpoint different from traditional antivirus tools?
Unlike traditional antivirus solutions that rely on signature-based detection, Microsoft Defender for Endpoint uses behavioral analysis, AI, and cloud intelligence to detect both known and unknown threats. It goes beyond basic protection by offering visibility into attack patterns, automated response actions, and cross-platform security, making it a complete endpoint security solution rather than just an antivirus tool.
How does Microsoft Defender use AI in cybersecurity?
Microsoft Defender leverages AI to analyze massive volumes of security data, identify anomalies, and correlate events into meaningful threat insights. It uses inputs from trillions of daily signals and global threat intelligence to detect patterns and automate responses, helping security teams act faster and reduce false positives while improving overall protection.
How much does Microsoft Defender for Endpoint cost?
Microsoft Defender for Endpoint is typically available as part of Microsoft’s security bundles rather than as a standalone product. For example, it is included in Microsoft 365 E3/E5 plans or the Microsoft Defender Suite, which can cost around ₹1,000 per user/month (India pricing) or about $12 per user/month annually, depending on the plan and features included. Pricing varies based on licensing, organization size, and additional modules.
Is Microsoft Defender for Endpoint suitable for small and mid-sized businesses?
Yes, Microsoft Defender for Endpoint is suitable for SMBs as well as large enterprises because it offers scalable plans and integrates easily with existing Microsoft ecosystems. Smaller businesses benefit from simplified deployment and automated protection, while larger organizations gain advanced features like threat hunting, exposure management, and enterprise-grade security controls.
Who should use Microsoft Defender for Endpoint?
Microsoft Defender for Endpoint is ideal for enterprises, SaaS companies, IT teams, and organizations that rely heavily on Microsoft infrastructure. It is particularly valuable for businesses that want integrated security across endpoints, identities, and cloud environments without managing multiple disconnected tools, making it a strong choice for organizations prioritizing unified and AI-driven cybersecurity.
User Reviews
No reviews yet for Microsoft Defender for Endpoint.
Featured Tools
Featured AI tools from TechShark
Melody Genie
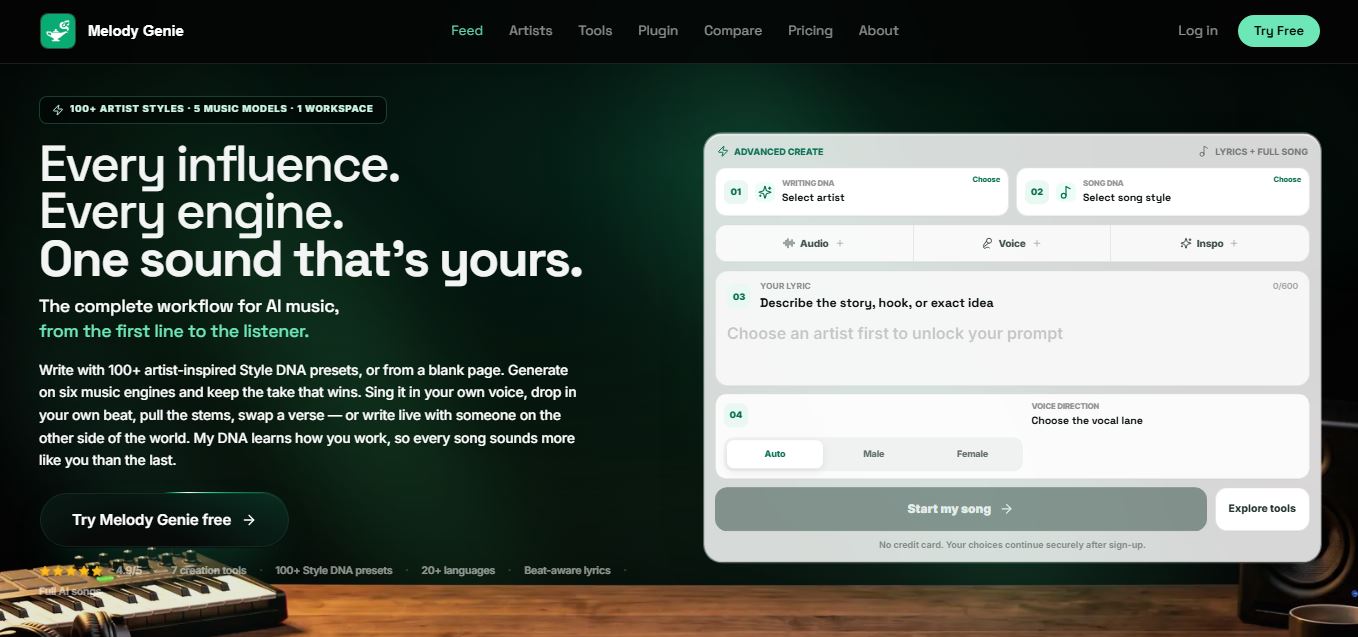
MelodyGenie is an AI-powered music generator that creates original songs from simple text prompts. Users can choose styles, moods, and genres, then instantly generate melodies and full tracks, making it easy for creators, marketers, and hobbyists to produce custom music without musical expertise.
Freemium
Kimi AI
Kimi AI is an advanced AI assistant developed by Moonshot AI that helps you chat, research, write, code, and automate tasks in one place. It supports web search, file analysis, and multimodal inputs, and can even run autonomous “agent” workflows to complete complex tasks end-to-end.
Freemium
Fashion Diffusion AI
Fashion Diffusion is an AI-powered fashion design platform that helps brands and designers create clothing designs, virtual try-ons, AI models, product photos, and marketing visuals faster and cost-effectively.
Paid
Veo 4
Veo 4 AI is an AI video creation platform that generates dramatic videos from text, images, audio, and video prompts using realistic motion and synchronized sound.
Paid
Alternatives
Alternatives to Microsoft Defender for Endpoint
The best Microsoft Defender for Endpoint alternatives include CrowdStrike Falcon, SentinelOne, Huntress, Sophos Intercept X, Palo Alto Networks Cortex XDR, and Trend Micro Vision One. These platforms provide endpoint detection and response (EDR), extended detection and response (XDR), and vulnerability management. While Microsoft Defender for Endpoint specializes in native Windows OS integration, automated incident remediation (AIR), and cost-effective bundling within Microsoft 365 E5 licensing, alternatives like CrowdStrike Falcon lead in specialized adversary threat intelligence, and SentinelOne focuses on autonomous on-agent rollback. Choosing the right tool depends on whether you have an existing Microsoft 365 ecosystem, require standalone multi-OS adversary defense, or want a 24/7 human managed SOC.
 4.9
Cisco
Cybersecurity
Cisco is a global networking and cybersecurity platform that helps businesses connect, secure, and manage applications, users, and data across cloud and on-prem environments. It combines networking, security, and observability solutions to deliver reliable infrastructure, improve performance, and protect modern digital operations at scale.
 4.9
IRONSCALES
Cybersecurity
IRONSCALES is an AI-powered email security platform that helps businesses detect, prevent, and respond to phishing, business email compromise, and account takeover attacks. It combines adaptive AI with human insights to automatically analyze, remediate threats, and protect inboxes in real time across Microsoft 365 and Google Workspace.
 4.9
Abnormal Security
Cybersecurity
Abnormal AI is an AI-powered behavioral cybersecurity platform that helps businesses detect and stop advanced threats like phishing, account takeovers, and social engineering. It learns normal user behavior across email, identity, and cloud systems, then automatically identifies anomalies and responds in real time to prevent attacks.
 4.9
Proofpoint
Cybersecurity
Proofpoint is an AI-powered cybersecurity and compliance platform that helps businesses protect people, data, and communications from threats like phishing, email attacks, and data breaches. It uses advanced threat intelligence and automation to detect risks, prevent data loss, and secure interactions across email, cloud, and collaboration tools.
 4.9
Zscaler
Cybersecurity
Zscaler is an AI-powered cloud security platform that uses zero trust architecture to protect users, applications, and data across the internet and cloud. It replaces traditional VPNs and firewalls, enabling secure access, real-time threat protection, and simplified security operations for modern, distributed businesses.
 5.0
Fortinet
Cybersecurity
Fortinet is an AI-powered cybersecurity platform that helps businesses protect networks, cloud systems, endpoints, and data through a unified security approach. Its Security Fabric integrates threat detection, response, and automation, giving organizations real-time visibility and protection while simplifying security operations across complex digital environments.
 4.9
Sophos
Cybersecurity
Sophos is an AI-powered cybersecurity platform that helps businesses prevent, detect, and respond to threats across endpoints, networks, cloud, and email systems. It combines automated protection with 24/7 managed detection and response, enabling organizations to stop attacks faster and maintain strong, unified security across environments.
 4.9
SentinelOne
Cybersecurity
SentinelOne is an AI-powered cybersecurity platform that helps businesses detect, prevent, and respond to threats across endpoints, cloud, identity, and AI systems. Its Singularity platform uses autonomous AI to stop attacks in real time, reduce manual work, and provide unified security visibility.
 4.9
CrowdStrike Falcon
Cybersecurity
CrowdStrike is an AI-powered cybersecurity platform that helps businesses detect, prevent, and respond to threats across endpoints, cloud, identity, and data. Its Falcon platform uses real-time intelligence and automation to stop breaches, reduce risk, and provide unified security visibility across modern digital environments.