CrowdStrike Falcon
CrowdStrike is an AI-powered cybersecurity platform that helps businesses detect, prevent, and respond to threats across endpoints, cloud, identity, and data. Its Falcon platform uses real-time intelligence and automation to stop breaches, reduce risk, and provide unified security visibility across modern digital environments.
What is CrowdStrike Falcon?
CrowdStrike Falcon is the global market-leading cloud-native cybersecurity and cross-domain unified agentic security platform. Engineered for Chief Information Security Officers (CISOs), Security Operations Centers (SOCs), IT directors, and enterprise security architects, Falcon stops digital breaches by converging next-generation endpoint security (EPP/EDR/XDR), Cloud-Native Application Protection (CNAPP), identity threat protection (ITDR), Next-Gen SIEM, and vulnerability management into a single, cloud-delivered platform. Instead of forcing organizations to deploy multiple conflicting security agents, CrowdStrike operates via a single lightweight kernel/user sensor backed by the multi-petabyte CrowdStrike Threat Graph and Charlotte AI reasoning engine.
Founded in 2011 by former McAfee executives George Kurtz and Gregg Bernstein in Sunnyvale, California (headquartered in Austin, Texas), CrowdStrike is a publicly traded global cybersecurity titan (NASDAQ: CRWD) with annual recurring revenue exceeding $4 billion. Holding leadership rankings across multiple consecutive Gartner Magic Quadrants for Endpoint Protection Platforms and Cyberthreat Intelligence, CrowdStrike protects over 29,000 corporate customers globally—including more than half of the Fortune 500 and the world's top banking and technology institutions. Processing trillions of security events daily, the Falcon platform pairs autonomous AI behavioral prevention with 24/7 human threat-hunting teams via Falcon OverWatch and Falcon Complete MDR.
- Founder / Leadership: George Kurtz (Co-founder, President & CEO)
- Launch Year: 2011 / 2012 (Public IPO in 2019)
Use Cases:
- Neutralizing fileless malware, script-based attacks, living-off-the-land binaries (LOLBins), and sophisticated ransomware campaigns in real time
- Safeguarding multi-cloud and container environments across AWS, Azure, and Google Cloud with unified agent and agentless posture checks (CNAPP)
- Defending Active Directory and cloud identities against credential stuffing, token theft, privilege escalation, and lateral movement
- Replacing slow, expensive legacy SIEM log lakes with high-speed Falcon Next-Gen SIEM and LogScale petabyte indexing
Technology:
- Single lightweight Falcon sensor capturing high-fidelity system telemetry across Windows, macOS, Linux, and mobile OS
- CrowdStrike Security Cloud & Threat Graph correlating trillions of daily events with real-time adversary attribution and MITRE ATT&CK mappings
- Charlotte AI AgentWorks and Agentic SOAR orchestrating autonomous SOC analyst reasoning, investigation canvases, and no-code agent building
Target Users:
- Chief Information Security Officers (CISOs) and enterprise SecOps leads managing global enterprise security postures
- Tier 1-3 SOC analysts, incident response teams, and cyber threat hunters conducting rapid forensic investigations
- Cloud security engineers and DevSecOps professionals securing CI/CD pipelines, Kubernetes clusters, and cloud workloads
- Content creators using writing tools to draft incident response playbooks, security disclosure statements, and enterprise compliance audits
Corporate Entity: Operates as CrowdStrike Holdings, Inc. (Austin, TX & Global)
Key features of CrowdStrike Falcon
CrowdStrike Falcon's key features are
- Single Lightweight Sensor: One universal cloud-native agent delivers endpoint protection, device control, firewall management, EDR, identity telemetry, and vulnerability assessment without signature updates or system reboots.
- Falcon Insight XDR & Real-Time EDR: Continuous kernel-level recording and behavioral telemetry mapping adversary actions to the MITRE ATT&CK matrix for instant lateral-movement detection and host isolation.
- Charlotte AI & AgentWorks: An autonomous generative and agentic AI SOC copilot triages incoming alerts with over 98% accuracy, creates no-code security agents, and visualizes cross-domain incident canvases.
- Falcon Identity Threat Protection (ITDR): Stops modern credential-based intrusions and pass-the-hash attacks with real-time risk scoring, behavioral Active Directory inspection, and conditional MFA challenges.
- Falcon Cloud Security (CNAPP): Unified agent and agentless protection safeguarding virtual machines, AWS, Azure, and GCP workloads, containers, and Kubernetes clusters from code to runtime.
- Falcon Next-Gen SIEM & LogScale: High-speed petabyte-scale log ingestion and search that parses first-party and 300+ third-party data sources dozens of times faster than legacy log tools.
- Falcon OverWatch (Proactive Threat Hunting): Elite 24/7 human threat-hunting division working continuously in parallel with AI models to catch stealthy, evasive intrusions.
- Falcon Complete Next-Gen MDR: Fully turnkey managed detection and response service where CrowdStrike experts take over triage, containment, and hands-on remediation, backed by a $1M breach warranty.
CrowdStrike Falcon Pricing
CrowdStrike Falcon offers transparent entry tiers for small-to-midsize businesses alongside modular FalconFlex portfolio licensing for mid-market and global enterprise organizations.
Public Small-to-Midsize Business Tiers:
- Falcon Go: $59.99 per device/year (Next-Gen Antivirus, USB Device Control, Mobile Security, 15-day free trial available)
- Falcon Pro: $99.99 per device/year (Adds Host Firewall Management and Threat Intelligence feeds)
- Falcon Enterprise: $184.99 per device/year (Adds full Falcon Insight XDR/EDR and Falcon OverWatch 24/7 managed threat hunting)
Falcon Complete MDR & Enterprise FalconFlex:
- Falcon Complete (MDR): Typically ranges between $200 and $400 per endpoint/year (or ~$25 to $45/endpoint/month based on scale), including turnkey 24/7 human-led remediation and up to a $1,000,000 breach warranty
- FalconFlex Licensing: Flexible enterprise contract model allowing organizations (typically 2,000+ endpoints) to draw down from a committed licensing pool and swap modules dynamically (Cloud, Identity, SIEM, EDR) as operational needs change
Disclaimer: Falcon Go, Pro, and Enterprise tiers require minimum device commitments. Enterprise modules (Cloud, Next-Gen SIEM, Identity) and Falcon Complete require custom scoping. Visit crowdstrike.com/en-us/pricing/ for up-to-date quotes.
Who is using CrowdStrike Falcon?
CrowdStrike Falcon is designed for enterprise organizations and security teams across every vertical, including
- Fortune 500 Enterprises & Global Corporations: Standardizing threat detection across hundreds of thousands of distributed global endpoints and servers
- Commercial Banks & Financial Services: Stopping identity-based attacks, credential abuse, and meeting strict FFIEC, SOC 2, and PCI-DSS compliance
- Healthcare Systems & Hospitals: Defending patient management databases, medical IoT devices, and clinical workstations against targeted ransomware
- Government & Defense Contractors: Securing sensitive public sector data with FedRAMP High and state-level authorized cloud environments
- Content Creators: Using writing tools to draft incident response playbooks, security disclosure statements, and enterprise compliance audits
- Mid-Market IT Teams: Relying on Falcon Complete to run a fully outsourced, tier-1 24/7 Security Operations Center without enterprise hiring overhead
Best CrowdStrike Falcon Alternatives
Some of the strongest CrowdStrike Falcon alternatives include
- SentinelOne
- Microsoft Defender for Endpoint
- Huntress
- Palo Alto Networks Cortex XDR
- Sophos Intercept X
- Trend Micro Vision One
Pros and Cons of CrowdStrike Falcon
Pros
- Market-leading threat detection efficacy powered by the world's richest adversary intelligence dataset and Threat Graph
- True single-sensor architecture unifies EDR, identity protection, cloud workloads, and next-gen SIEM without agent bloat
- Falcon OverWatch and Falcon Complete deliver exceptional 24/7 human-led threat hunting and hands-off incident remediation
- Charlotte AI AgentWorks provides cutting-edge agentic SOC automation and natural-language incident triage
- FalconFlex licensing allows enterprises to adaptively swap security modules without renegotiating static contracts
Cons
- Premium pricing structure commands a significant cost premium compared to basic antivirus and mid-market competitors
- Advanced enterprise modules (Next-Gen SIEM, Identity Threat Protection, Cloud Security) require custom enterprise agreements
- Deep feature breadth and extensive policy matrices present a steep learning curve for solo sysadmins without dedicated security training
- Relies heavily on continuous cloud connectivity to unlock full Threat Graph correlations and Charlotte AI agentic reasoning
Why Choose CrowdStrike Falcon?
CrowdStrike Falcon is the premier choice for organizations that need the highest caliber of breach prevention, adversary intelligence, and cross-domain security available today.
- Proven track record stopping sophisticated nation-state adversaries and ransomware cartels
- Consolidates fragmented endpoint, cloud, identity, and SIEM point tools onto a single platform
- Reduces SOC workload with Charlotte AI autonomous triage and agentic SOAR capabilities
- Provides complete peace of mind with 24/7 OverWatch hunting and Falcon Complete's $1M breach warranty
- Recognized by Gartner, Forrester, and IDC as the dominant leader in modern endpoint security
CrowdStrike Falcon vs. Competitors
The main difference between CrowdStrike Falcon, SentinelOne, Microsoft Defender, and Huntress is that CrowdStrike delivers an all-domain agentic security platform powered by elite adversary intelligence and a single unified sensor spanning EDR, identity, cloud, and next-gen SIEM, whereas SentinelOne emphasizes automated on-agent behavioral AI, Microsoft Defender relies on tight native Windows OS integration within M365 licensing, and Huntress specializes in accessible 24/7 human SOC management tailored for SMBs and MSPs. CrowdStrike stands out for its adversary intelligence depth, enterprise scalability, and comprehensive Falcon Complete MDR services.
| Feature / Tool | CrowdStrike Falcon (crowdstrike.com) | SentinelOne Singularity | Microsoft Defender for Endpoint | Huntress |
|---|---|---|---|---|
| Core Focus | AI-Native EDR, XDR & Unified Agentic SOC | Autonomous On-Agent Behavioral XDR | Native Windows & M365 Security Suite | Managed EDR & 24/7 SOC for SMB/MSP |
| Agent Architecture | Single Lightweight Cloud Sensor | Single Autonomous Agent | Built into Windows OS / Agent for others | Lightweight Host Agent + Cloud |
| Threat Hunting / MDR | OverWatch & Falcon Complete MDR | Vigilance MDR Add-on | Microsoft Defender Experts (Add-on) | 24/7 Human SOC Included by Default |
| AI SOC Analyst | Charlotte AI & AgentWorks | Purple AI Copilot | Security Copilot (Add-on) | SOC Investigation Automation |
| Starting Paid Price | $59.99/device/year (Falcon Go) | ~$45.00–$70.00/endpoint/year | Included in M365 E5 or ~$3-$5/user/mo | Custom Flat SMB/MSP Pricing |
| Best For | Global Enterprise & Mission-Critical XDR | Autonomous On-Device Remediation | Windows-Heavy Enterprise Stacks | SMBs, MSPs & Lean Corporate IT |
How do we rate CrowdStrike Falcon?
| Parameter | Rating (out of 5) |
|---|---|
| Threat Prevention & EDR/XDR Precision | 5.0 |
| Adversary Intelligence & OverWatch Hunting | 5.0 |
| Single-Sensor Architecture & Platform Breadth | 4.9 |
| Charlotte AI & Agentic SOC Capabilities | 4.9 |
| Value for Money | 4.7 |
| Overall Score | 4.90 |
CrowdStrike Falcon Review
CrowdStrike Falcon remains the gold standard in enterprise cybersecurity. While legacy security vendors struggled for years to patch together disparate acquisitions with multiple desktop agents and heavy signature files, CrowdStrike pioneered the single-agent, cloud-native architecture that defines the modern industry. Its Threat Graph and adversary intelligence capabilities provide unparalleled visibility into advanced attacker tradecraft, enabling organizations to stop intrusions before lateral movement occurs. The integration of Charlotte AI and AgentWorks elevates operational efficiency further, automating routine alert triage and empowering defenders to orchestrate an agentic SOC at machine speed. For enterprises seeking proven breach defense and cross-domain visibility, CrowdStrike Falcon is an exceptional platform.
Conclusion
CrowdStrike Falcon is an industry-leading cybersecurity and unified agentic security platform that redefines how organizations defend endpoints, cloud workloads, identities, and data lakes. By combining a single lightweight sensor, behavioral AI detection, Charlotte AI agentic orchestration, and elite 24/7 human threat hunters into an integrated cloud architecture, it eliminates the chaos of vendor sprawl. While smaller businesses must evaluate licensing minimums and premium module costs, CrowdStrike Falcon’s detection accuracy, enterprise scalability, and proven adversary defense make it an indispensable cybersecurity platform.
FAQ
What is CrowdStrike and how does it work?
CrowdStrike is an AI-native cybersecurity platform that protects organizations across endpoints, cloud workloads, identities, and data. It works through its Falcon platform, which uses a single lightweight agent installed on devices to collect security data and send it to the cloud. This data is then analyzed using AI and threat intelligence to detect, investigate, and automatically respond to cyber threats in real time.
What problems does CrowdStrike solve?
CrowdStrike helps businesses address modern cybersecurity challenges such as ransomware attacks, advanced persistent threats, and identity-based breaches. Traditional tools often miss complex or AI-driven attacks, but CrowdStrike provides unified visibility and automated response across systems, helping organizations detect threats faster and stop breaches before they cause damage.
What features does CrowdStrike offer?
CrowdStrike offers a wide range of features through its Falcon platform, including next-generation antivirus, endpoint detection and response (EDR), extended detection and response (XDR), identity protection, threat intelligence, SIEM capabilities, and managed detection and response (MDR). It also includes capabilities like automated remediation, AI-driven investigations, and cloud and container security, all delivered through a unified platform.
How is CrowdStrike different from traditional security tools?
CrowdStrike differs from traditional security tools by being cloud-native and AI-driven, eliminating the need for heavy on-premise infrastructure. Instead of using multiple disconnected tools, it provides a single platform with a lightweight agent and centralized intelligence. This approach reduces complexity, improves scalability, and enables faster detection and response compared to legacy antivirus or endpoint solutions.
How does CrowdStrike use AI in cybersecurity?
CrowdStrike uses AI to analyze massive amounts of security data, identify attack patterns, and automate threat detection and response. Its AI models are trained on real-world adversary behavior and enriched with threat intelligence, enabling faster and more accurate detection while reducing false positives. This allows security teams to respond to threats at machine speed instead of relying on manual processes.
How much does CrowdStrike cost?
CrowdStrike follows a subscription-based pricing model with different Falcon bundles. Entry-level plans like Falcon Go start at around $7.99 per device per month, while more advanced plans such as Falcon Pro and Enterprise cost approximately $14.99 to $19.99 per device per month, with enterprise-grade and managed solutions priced via custom quotes. Pricing depends on the features, modules, and scale of deployment.
Is CrowdStrike suitable for small and mid-sized businesses?
Yes, CrowdStrike offers scalable solutions that work for both small businesses and large enterprises. With flexible pricing tiers and cloud-native deployment, SMBs can start with basic protection and scale up as needed. The platform’s ease of deployment and automation also makes it suitable for organizations without large in-house security teams.
Who should use CrowdStrike?
CrowdStrike is ideal for enterprises, SaaS companies, startups, and managed service providers that require strong, modern cybersecurity protection. It is particularly valuable for organizations dealing with sensitive data or facing advanced cyber threats, as it provides unified visibility, AI-driven protection, and real-time response across multiple environments.
User Reviews
No reviews yet for CrowdStrike Falcon.
Featured Tools
Featured AI tools from TechShark
Melody Genie
MelodyGenie is an AI-powered music generator that creates original songs from simple text prompts. Users can choose styles, moods, and genres, then instantly generate melodies and full tracks, making it easy for creators, marketers, and hobbyists to produce custom music without musical expertise.
Freemium
Kimi AI
Kimi AI is an advanced AI assistant developed by Moonshot AI that helps you chat, research, write, code, and automate tasks in one place. It supports web search, file analysis, and multimodal inputs, and can even run autonomous “agent” workflows to complete complex tasks end-to-end.
Freemium
Fashion Diffusion AI
Fashion Diffusion is an AI-powered fashion design platform that helps brands and designers create clothing designs, virtual try-ons, AI models, product photos, and marketing visuals faster and cost-effectively.
Paid
Veo 4
Veo 4 AI is an AI video creation platform that generates dramatic videos from text, images, audio, and video prompts using realistic motion and synchronized sound.
Paid
Alternatives
Alternatives to CrowdStrike Falcon
The best CrowdStrike Falcon alternatives include SentinelOne (Singularity Platform), Microsoft Defender for Endpoint, Huntress, Palo Alto Networks Cortex XDR, Sophos Intercept X, and Trend Micro Vision One. These platforms provide endpoint protection, extended detection and response (XDR), and managed detection services. While CrowdStrike Falcon specializes in a single-sensor architecture backed by adversary intelligence, Charlotte AI agentic SOC orchestration, and Falcon Complete MDR, alternatives like SentinelOne focus on autonomous on-agent behavioral AI, and Huntress delivers a human-led 24/7 SOC tailored for SMBs and MSPs. Choosing the right tool depends on whether you require an all-domain enterprise breach prevention suite, autonomous endpoint response, or an SMB-friendly managed SOC.
 4.9
Vectra AI
Cybersecurity
Vectra AI is an AI-powered cybersecurity platform that helps businesses detect, investigate, and stop attacks across network, identity, and cloud environments. It uses behavioral analytics to identify real attacker activity, reduce alert noise, and provide clear, real-time insights so security teams can respond faster and prevent breaches.
 4.9
Darktrace
Cybersecurity
Darktrace is an AI-powered cybersecurity platform that helps businesses detect, investigate, and respond to cyber threats in real time. It uses self-learning AI to understand normal behavior across networks, cloud, and users, identifying anomalies and stopping advanced attacks before they cause damage.
 4.9
Cisco
Cybersecurity
Cisco is a global networking and cybersecurity platform that helps businesses connect, secure, and manage applications, users, and data across cloud and on-prem environments. It combines networking, security, and observability solutions to deliver reliable infrastructure, improve performance, and protect modern digital operations at scale.
 4.9
IRONSCALES
Cybersecurity
IRONSCALES is an AI-powered email security platform that helps businesses detect, prevent, and respond to phishing, business email compromise, and account takeover attacks. It combines adaptive AI with human insights to automatically analyze, remediate threats, and protect inboxes in real time across Microsoft 365 and Google Workspace.
 4.9
Abnormal Security
Cybersecurity
Abnormal AI is an AI-powered behavioral cybersecurity platform that helps businesses detect and stop advanced threats like phishing, account takeovers, and social engineering. It learns normal user behavior across email, identity, and cloud systems, then automatically identifies anomalies and responds in real time to prevent attacks.
 4.9
Proofpoint
Cybersecurity
Proofpoint is an AI-powered cybersecurity and compliance platform that helps businesses protect people, data, and communications from threats like phishing, email attacks, and data breaches. It uses advanced threat intelligence and automation to detect risks, prevent data loss, and secure interactions across email, cloud, and collaboration tools.
 4.9
Zscaler
Cybersecurity
Zscaler is an AI-powered cloud security platform that uses zero trust architecture to protect users, applications, and data across the internet and cloud. It replaces traditional VPNs and firewalls, enabling secure access, real-time threat protection, and simplified security operations for modern, distributed businesses.
 5.0
Fortinet
Cybersecurity
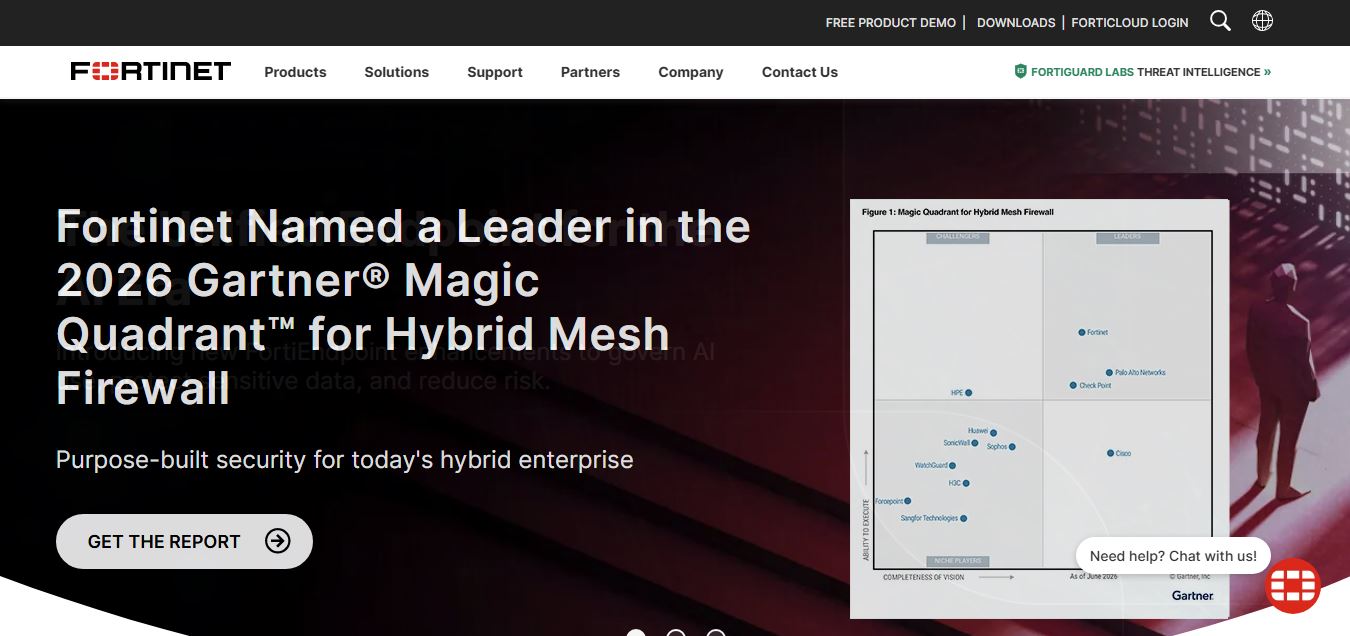
Fortinet is an AI-powered cybersecurity platform that helps businesses protect networks, cloud systems, endpoints, and data through a unified security approach. Its Security Fabric integrates threat detection, response, and automation, giving organizations real-time visibility and protection while simplifying security operations across complex digital environments.
 4.9
Sophos
Cybersecurity
Sophos is an AI-powered cybersecurity platform that helps businesses prevent, detect, and respond to threats across endpoints, networks, cloud, and email systems. It combines automated protection with 24/7 managed detection and response, enabling organizations to stop attacks faster and maintain strong, unified security across environments.