Huntress
Huntress is an AI-powered managed cybersecurity platform that helps businesses detect, investigate, and stop threats across endpoints and identities. It combines automated threat detection with a 24/7 security operations team, handling everything from alert analysis to remediation so organizations stay protected without managing complex security tools.
What is Huntress?
Huntress is an AI-powered cybersecurity platform that helps businesses detect, respond to, and eliminate cyber threats across endpoints, identities, and systems. It combines automated detection tools with a 24/7 Security Operations Center (SOC) run by expert threat hunters, who actively investigate and remediate attacks in real time. The platform includes capabilities like endpoint detection and response (EDR), identity threat protection, and managed SIEM, making enterprise-grade security accessible without complex setups.
Founded in 2015 by former U.S. National Security Agency (NSA) Cyber Operators Kyle Hanslovan and Chris Bisnett in Columbia, Maryland, Huntress was engineered with deep Department of Defense offensive cyber tradecraft. Backed by premier venture capital firms including Kleiner Perkins, Meritech Capital, Sapphire Ventures, and ForgePoint Capital, the company has raised over $300 million in total funding, achieving a valuation of $1.6 billion and surpassing $100M+ in annual recurring revenue (ARR). Protecting over 105,000 organizations and more than 4 million endpoints globally, Huntress isolates compromised hosts and delivers actionable, single-click remediation playbooks directly to IT administrators.
- Founder / Leadership: Kyle Hanslovan (Co-founder & CEO) and Chris Bisnett (Co-founder & CTO)
- Launch Year: 2015
Use Cases:
- Detecting and evicting persistent footholds, living-off-the-land binaries (LOLBins), and hidden ransomware before encryption starts
- Safeguarding Microsoft 365 environments against business email compromise (BEC), malicious inbox forwarding rules, and suspicious logins
- Consolidating multi-tenant event logs into a cloud-native managed SIEM for compliance audit reporting without on-premise hardware
- Delivering engaging, story-driven employee cybersecurity awareness and automated phishing simulations via Huntress SAT (Curricula)
Technology:
- Continuous endpoint sensor capturing process trees, autoruns, scheduled tasks, and lateral movement telemetry
- Human-in-the-loop 24/7 Security Operations Center (SOC) analyzing ambiguous signals and filtering out false positives
- Multi-tenant cloud management fabric enabling MSPs and IT teams to orchestrate remediation across thousands of accounts
Target Users:
- Managed Service Providers (MSPs) and MSSPs seeking scalable, high-margin cybersecurity services with zero alert fatigue
- Internal IT directors and sysadmins managing 50 to 5,000 endpoints without dedicated in-house cybersecurity specialists
- Compliance and risk officers fulfilling cyber insurance criteria and frameworks like NIST CSF, HIPAA, and CIS Controls
- Content creators using writing tools to draft incident response plans, employee security policies, and cybersecurity compliance reports
Corporate Entity: Operates as Huntress Labs Inc. (Columbia, MD)
Key features of Huntress
Huntress's key features are
- 24/7 Human-Led Security Operations Center: Elite threat analysts evaluate suspicious activity, weed out false positives, and compile contextual incident reports with step-by-step remediation plans.
- Managed EDR (Endpoint Detection & Response): Deep process-level telemetry monitoring Windows, macOS, and Linux endpoints to neutralize malware, fileless scripts, and ransomware footholds.
- Managed ITDR for Microsoft 365: Monitors user logins, privilege escalation, token theft, and anomalous inbox forwarding rules to combat Business Email Compromise (BEC).
- Managed Cloud-Native SIEM: Collects and correlates security event logs across network endpoints, cloud directories, and SaaS without demanding heavy local hardware collectors.
- Persistent Foothold Hunting: Specializes in rooting out hidden startup persistence mechanisms, unauthorized registry run keys, and scheduled tasks that bypass standard antivirus.
- Host Isolation & Assisted Remediation: Sever network connectivity on compromised machines in one click while preserving cloud communication for SOC investigation and guided repair.
- Managed Security Awareness Training (SAT): Built on the acquired Curricula platform, delivering animated story-based phishing simulations and employee behavioral training.
- Multi-Tenant Partner Console: Engineered for MSPs with native integrations into ConnectWise, Datto/Autotask, Kaseya, HaloPSA, Syncro, and Liongard.
Huntress Pricing
Huntress operates on a flat, transparent per-unit subscription model based on managed endpoints, Microsoft 365 user identities, and SIEM data sources, with 24/7 SOC analysis included in all platform products.
MSP & Reseller Partner Pricing:
- Tiered volume discounts based on aggregate endpoints and identities under management across all client tenants
- No long-term lock-in contracts or forced upfront licensing commitments for qualifying channel partners
Direct Commercial / Mid-Market Pricing:
- Managed EDR: Typically ranges from approximately $2.50 to $4.50 per endpoint/month depending on fleet volume
- Managed ITDR (M365): Starting from approximately $1.50 to $3.00 per protected user identity/month
- Managed SIEM: Flat-rate billing per integrated data source, eliminating punitive per-gigabyte log overage penalties
- Security Awareness Training (SAT): Scaled per active training learner/month
Disclaimer: Huntress includes 24/7 SOC management across all products without hidden surcharge tiers. For tailored fleet evaluations, partner margins, and custom mid-market quotes, visit huntress.com/pricing.
Who is using Huntress?
Huntress is designed for IT service providers and lean corporate IT organizations, including
- Managed Service Providers (MSPs): Protecting hundreds of disparate SMB client accounts from a single centralized multi-tenant console
- Mid-Market Corporate IT Teams: Gaining enterprise-level MDR and 24/7 SOC capabilities without recruiting expensive round-the-clock analysts
- Healthcare Clinics & Regional Hospitals: Defending sensitive patient records and medical workstations against targeted ransomware outbreaks
- Financial & Legal Practices: Safeguarding executive Microsoft 365 accounts from unauthorized wire-fraud redirection schemes
- Content Creators: Using writing tools to draft incident response plans, employee security policies, and cybersecurity compliance reports
- Educational Districts & Municipalities: Securing public infrastructure with simple agent deployment and assisted remediation
Best Huntress Alternatives
Some of the strongest Huntress alternatives include
- CrowdStrike Falcon
- SentinelOne
- Blackpoint Cyber
- Sophos MDR
- Blumira
- Arctic Wolf
Pros and Cons of Huntress
Pros
- 24/7 human SOC management is included by default across all products—eliminating noisy alerts and false positives
- Single-click assisted remediation delivers explicit instructions and scripts to resolve intrusions instantly
- Industry leader in multi-tenant management, PSA integrations, and partner support for MSPs
- Cloud-native Managed SIEM uses flat data-source pricing without unpredictable per-GB log billing spikes
- Deep expertise from former NSA cyber operators actively tracking emergent threat tradecraft in real time
Cons
- Requires a minimum fleet commitment for direct corporate accounts, steering very small teams to MSP partners
- Does not attempt to provide an on-premise hardware firewall or network gateway appliance
- Managed ITDR coverage is currently specialized around Microsoft 365, with Google Workspace identity modules evolving
- Enterprise organizations requiring complete in-house control over raw SIEM ingestion code may prefer complex SIEM platforms
Why Choose Huntress?
Huntress is the premier choice for organizations and service providers that want real cybersecurity outcomes backed by human expertise rather than empty automation promises.
- Combines algorithmic endpoint agents with real human cyber operators who investigate every critical incident
- Eliminates alert fatigue by sending clear, verified remediation playbooks instead of raw telemetry
- Protects both endpoint machines and cloud identities across Microsoft 365 environments
- Engineered natively for MSPs with seamless PSA ticketing and multi-tenant management
- Backed by Tier-1 cybersecurity venture capital, a $1.6B valuation, and trusted by over 100,000 businesses
Huntress vs. Competitors
The main difference between Huntress, CrowdStrike Falcon Complete, SentinelOne Vigilance, and Blackpoint Cyber is that Huntress is purpose-built for the SMB and MSP ecosystem, bundling human SOC management into an affordable flat-rate per-endpoint structure, whereas CrowdStrike and SentinelOne are enterprise-first EDR engines where full human MDR services command massive enterprise premiums. Blackpoint Cyber focuses on automated active defense for MSPs, but Huntress delivers broader converged identity, SIEM, and awareness training. Huntress stands out for its high-signal remediation and partner-first economics.
| Feature / Tool | Huntress (huntress.com) | CrowdStrike Falcon | SentinelOne | Blackpoint Cyber |
|---|---|---|---|---|
| Core Focus | Managed EDR, ITDR & SOC for SMB/MSP | Enterprise EDR & Cloud Security | Autonomous AI Endpoint Protection | Managed Active Defense for MSPs |
| 24/7 Human SOC | Included by Default | Premium Add-on (Complete) | Premium Add-on (Vigilance) | Included (MDR Service) |
| Microsoft 365 ITDR | Yes (Managed M365 Protection) | Identity Threat Protection Add-on | Singularity Identity Add-on | Cloud Response (M365) |
| Managed Cloud SIEM | Yes (Flat Data Source Pricing) | LogScale (Usage-based) | Singularity DataLake | Managed SIEM Add-on |
| Target Market | SMBs, MSPs & Mid-Market IT | Fortune 500 & Global Enterprise | Enterprise & Mid-Market | Dedicated MSP Channel |
| Starting Paid Price | Custom SMB/MSP Flat Rates | Enterprise Contracts ($60+/seat) | Enterprise Contracts ($45+/seat) | MSP Channel Volume Pricing |
How do we rate Huntress?
| Parameter | Rating (out of 5) |
|---|---|
| 24/7 Human SOC Analysis & Signal Clarity | 5.0 |
| Endpoint Detection & Foothold Isolation | 4.9 |
| Microsoft 365 Identity Protection (ITDR) | 4.9 |
| MSP Multi-Tenancy & PSA Integrations | 5.0 |
| Value for Money | 4.8 |
| Overall Score | 4.92 |
Huntress Review
Huntress has transformed modern cyber defense for the organizations that need it most. For years, the cybersecurity industry treated small and mid-sized enterprises as an afterthought, pitching automated antivirus engines that left overworked sysadmins drowning in alerts they had neither the time nor expertise to investigate. Huntress flipped this model on its head by coupling lightweight host telemetry with a dedicated 24/7 SOC staffed by elite analysts. When an incident occurs, administrators do not receive raw log traces; they receive a precise, validated incident report with an assisted one-click remediation button. With the successful addition of Microsoft 365 ITDR and cloud-native Managed SIEM, Huntress has evolved into an indispensable security backbone for tens of thousands of businesses and the MSPs that safeguard them.
Conclusion
Huntress is a market-leading managed cybersecurity platform that redefines how SMBs and MSPs combat modern cyber threats. By uniting Managed EDR, Microsoft 365 identity protection, flat-rate Managed SIEM, and Security Awareness Training with an elite 24/7 human SOC, it eliminates alert fatigue and delivers immediate threat containment. While enterprise conglomerates with massive internal SOC teams may select customizable enterprise SIEMs, Huntress’s human expertise, operational simplicity, and partner-friendly architecture make it an essential cybersecurity platform.
FAQ
What is Huntress and how does it work?
Huntress is a fully managed cybersecurity platform that protects businesses from threats across endpoints, identities, and cloud environments. It works by combining lightweight software agents with a 24/7 human-led Security Operations Center (SOC) that detects, investigates, and actively responds to threats on your behalf.
What problems does Huntress solve?
Huntress helps organizations solve issues like undetected cyber threats, lack of security expertise, and slow incident response. Instead of relying on internal teams alone, it provides continuous monitoring and remediation to stop attacks like ransomware, phishing, and account takeovers before they cause damage.
How is Huntress different from traditional security tools?
Unlike standalone tools, Huntress provides a fully managed approach—you don’t just get software, you get a team. Its SOC actively investigates alerts and handles detection → investigation → remediation, reducing the need for in-house security expertise.
How does Huntress use AI in cybersecurity?
Huntress uses AI within its SOC to analyze signals, correlate threats, and accelerate investigations. AI assists human analysts by filtering noise, identifying patterns, and helping respond to high-confidence threats faster.
Is Huntress suitable for small and mid-sized businesses?
Yes, Huntress is specifically designed for SMBs, startups, and growing organizations that need enterprise-grade security without building a large in-house security team. It’s also widely used by MSPs to manage client security at scale.
How is Huntress different from traditional security tools?
Huntress differs from traditional security tools by offering a fully managed approach rather than just standalone software. Instead of relying on internal teams to interpret alerts and take action, Huntress provides a dedicated SOC that handles detection, investigation, and remediation. This significantly reduces the burden on IT teams and ensures that threats are addressed quickly and effectively without requiring deep cybersecurity expertise in-house.
How much does Huntress cost?
Huntress follows a transparent, usage-based pricing model where businesses pay based on the number of endpoints, identities, or data sources they want to protect. For example, endpoint protection is typically priced per device per month, while identity protection and SIEM services are priced per user or data source. The cost includes access to the 24/7 SOC, which means organizations get both the technology and expert support without additional hidden fees.
Who should use Huntress?
Huntress is ideal for IT teams, managed service providers (MSPs), startups, and growing businesses that need reliable cybersecurity protection without building a full in-house SOC. It is particularly useful for organizations that handle sensitive data or operate in environments where security threats are frequent, as it offers hands-off protection with expert oversight and continuous monitoring.
User Reviews
No reviews yet for Huntress.
Featured Tools
Featured AI tools from TechShark
Melody Genie
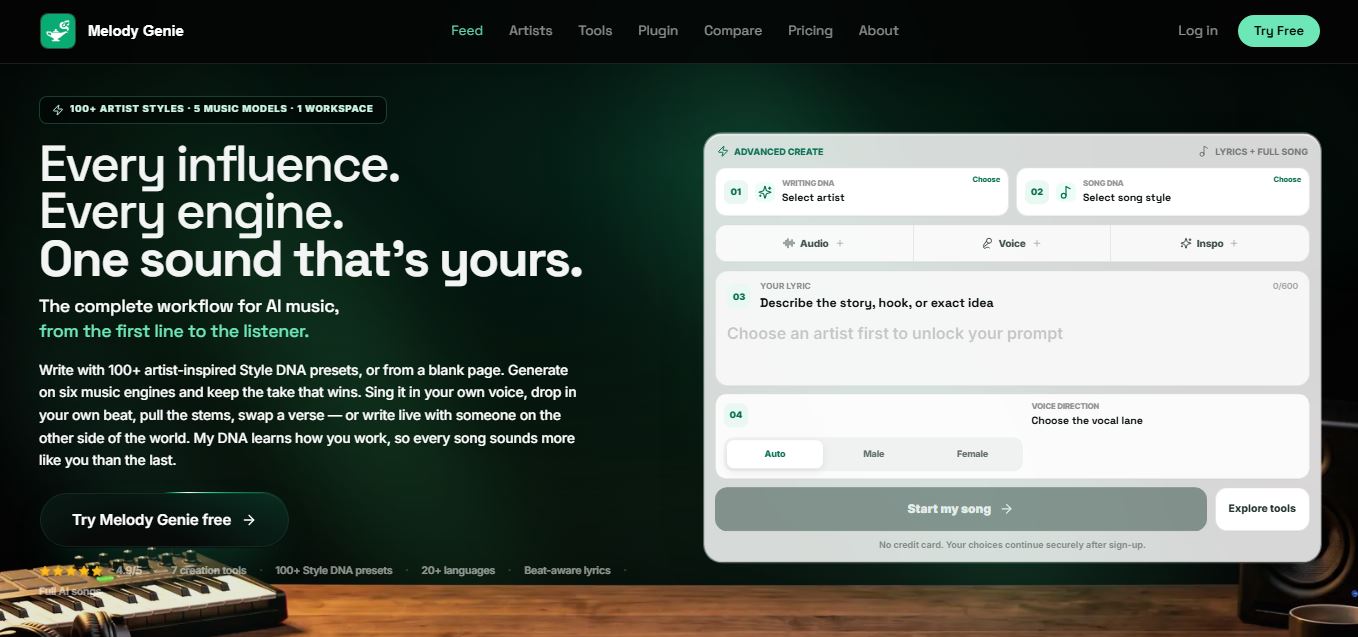
MelodyGenie is an AI-powered music generator that creates original songs from simple text prompts. Users can choose styles, moods, and genres, then instantly generate melodies and full tracks, making it easy for creators, marketers, and hobbyists to produce custom music without musical expertise.
Freemium
Kimi AI
Kimi AI is an advanced AI assistant developed by Moonshot AI that helps you chat, research, write, code, and automate tasks in one place. It supports web search, file analysis, and multimodal inputs, and can even run autonomous “agent” workflows to complete complex tasks end-to-end.
Freemium
Fashion Diffusion AI
Fashion Diffusion is an AI-powered fashion design platform that helps brands and designers create clothing designs, virtual try-ons, AI models, product photos, and marketing visuals faster and cost-effectively.
Paid
Veo 4
Veo 4 AI is an AI video creation platform that generates dramatic videos from text, images, audio, and video prompts using realistic motion and synchronized sound.
Paid
Alternatives
Alternatives to Huntress
The best Huntress alternatives include CrowdStrike Falcon, SentinelOne, Blackpoint Cyber, Sophos MDR, Blumira, and Arctic Wolf. These platforms provide endpoint detection, managed detection and response (MDR), and security information event management (SIEM). While Huntress specializes in an SMB- and MSP-tailored security operations platform bundling 24/7 human SOC analysis by default with flat-rate SIEM and Microsoft 365 ITDR, alternatives like CrowdStrike and SentinelOne focus on enterprise-level endpoint autonomy with add-on MDR services. Choosing the right tool depends on whether you require an all-in-one human SOC partner for MSPs and SMBs, automated enterprise endpoint controls, or high-volume enterprise log lakes.
 4.9
Cisco
Cybersecurity
Cisco is a global networking and cybersecurity platform that helps businesses connect, secure, and manage applications, users, and data across cloud and on-prem environments. It combines networking, security, and observability solutions to deliver reliable infrastructure, improve performance, and protect modern digital operations at scale.
 4.9
IRONSCALES
Cybersecurity
IRONSCALES is an AI-powered email security platform that helps businesses detect, prevent, and respond to phishing, business email compromise, and account takeover attacks. It combines adaptive AI with human insights to automatically analyze, remediate threats, and protect inboxes in real time across Microsoft 365 and Google Workspace.
 4.9
Abnormal Security
Cybersecurity
Abnormal AI is an AI-powered behavioral cybersecurity platform that helps businesses detect and stop advanced threats like phishing, account takeovers, and social engineering. It learns normal user behavior across email, identity, and cloud systems, then automatically identifies anomalies and responds in real time to prevent attacks.
 4.9
Proofpoint
Cybersecurity
Proofpoint is an AI-powered cybersecurity and compliance platform that helps businesses protect people, data, and communications from threats like phishing, email attacks, and data breaches. It uses advanced threat intelligence and automation to detect risks, prevent data loss, and secure interactions across email, cloud, and collaboration tools.
 4.9
Zscaler
Cybersecurity
Zscaler is an AI-powered cloud security platform that uses zero trust architecture to protect users, applications, and data across the internet and cloud. It replaces traditional VPNs and firewalls, enabling secure access, real-time threat protection, and simplified security operations for modern, distributed businesses.
 5.0
Fortinet
Cybersecurity
Fortinet is an AI-powered cybersecurity platform that helps businesses protect networks, cloud systems, endpoints, and data through a unified security approach. Its Security Fabric integrates threat detection, response, and automation, giving organizations real-time visibility and protection while simplifying security operations across complex digital environments.
 4.9
Sophos
Cybersecurity
Sophos is an AI-powered cybersecurity platform that helps businesses prevent, detect, and respond to threats across endpoints, networks, cloud, and email systems. It combines automated protection with 24/7 managed detection and response, enabling organizations to stop attacks faster and maintain strong, unified security across environments.
 4.9
Microsoft Defender for Endpoint
Security
Microsoft Defender for Endpoint is an AI-powered endpoint security platform that helps businesses prevent, detect, and respond to cyber threats across devices like laptops, servers, and mobile systems. It combines antivirus, threat intelligence, and automated response to stop attacks, reduce risk, and provide full visibility across environments.
 4.9
SentinelOne
Cybersecurity
SentinelOne is an AI-powered cybersecurity platform that helps businesses detect, prevent, and respond to threats across endpoints, cloud, identity, and AI systems. Its Singularity platform uses autonomous AI to stop attacks in real time, reduce manual work, and provide unified security visibility.