Veracode
Veracode is an enterprise application risk management and AppSec platform combining static analysis (SAST), dynamic testing (DAST), software composition analysis (SCA), container security, and AI-driven automated flaw remediation with Veracode Fix.
What is Veracode?
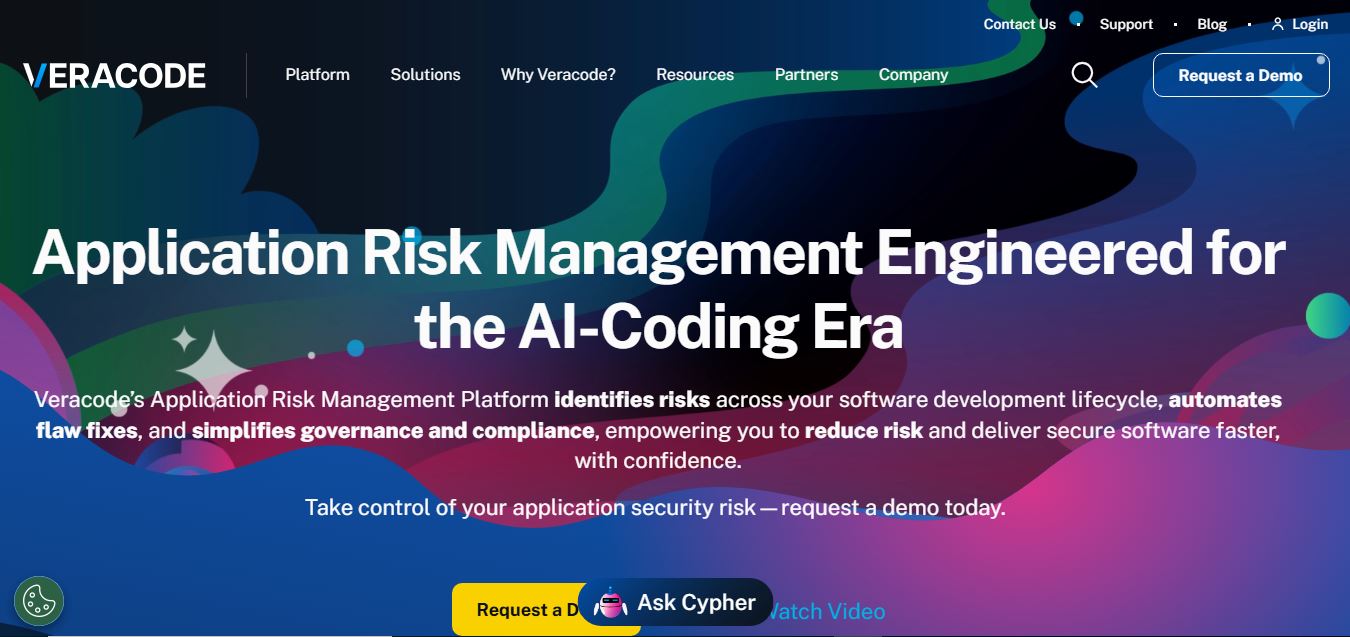
Veracode is an enterprise-grade application risk management and software security platform designed to secure code across the entire software development life cycle (SDLC). Founded by Chris Wysopal and Christien Rioux, Veracode provides comprehensive cloud-native AppSec tooling that enables organizations to uncover, prioritize, and remediate vulnerabilities in first-party source code, open-source libraries, container images, and running web applications.
Built around the vision of “Application Risk Management engineered for the AI-coding era,” Veracode bridges the gap between security governance and developer agility. Leveraging decades of proprietary vulnerability intelligence alongside machine learning, Veracode pairs deep security posture visibility with Veracode Fix—an AI-powered engine that automatically suggests curated code patches directly inside developer IDEs and CI/CD pipelines.
- Platform Role: Application Security Posture Management (ASPM), Multi-Vector Vulnerability Scanner & AI Code Remediation Engine
- Founders & Organization: Chris Wysopal and Christien Rioux (Veracode, Burlington, Massachusetts)
- Ecosystem Integrations: GitHub, GitLab, Bitbucket, Jenkins, Azure DevOps, Jira, VS Code, IntelliJ, and major container registries
Use Cases:
- Scanning source code during development via Static Application Security Testing (SAST) to identify security flaws before code commits
- Automatically generating curated patch diffs for identified vulnerabilities using Veracode Fix to reduce developer remediation backlogs
- Detecting open-source vulnerabilities and license compliance risks across the software supply chain through Software Composition Analysis (SCA)
- Uncovering runtime vulnerabilities and configuration missteps in live staging or production web apps via Dynamic Application Security Testing (DAST)
- Securing containerized workloads and base images before deployment to production cloud clusters
Technology:
- Proprietary binary and source code analysis engine delivering low false-positive rates (<1.1%) across dozens of programming languages
- Veracode Fix: specialized generative AI model trained on verified secure code datasets to generate curated flaw remediation code
- Comprehensive Application Security Posture Management (ASPM) framework delivering unified risk scoring and policy enforcement
- Package Firewall and software supply chain protection proactively blocking vulnerable dependencies from entering the repository
Target Users:
- Chief Information Security Officers (CISOs) and security directors requiring centralized policy governance and regulatory compliance reporting
- Application Security (AppSec) teams overseeing vulnerability triage and tracking risk across thousands of enterprise repos
- Software developers and DevSecOps engineers seeking instant vulnerability feedback and automated code fixes inside their IDEs
- Public sector and defense organizations requiring audited, FedRAMP-authorized application security environments
Acquisition: Global enterprise cybersecurity firm headquartered in Burlington, Massachusetts
What are the key features of Veracode?
Veracode's key platform features are
- Static Application Security Testing (SAST): Fast, deep analysis of proprietary source code and compiled binaries, catching architectural flaws early.
- Veracode Fix (AI Remediation): Suggests context-aware, ready-to-merge remediation patches for detected security flaws, dramatically accelerating remediation.
- Software Composition Analysis (SCA): Identifies vulnerable open-source dependencies, monitors Software Bill of Materials (SBOMs), and tracks legal licensing risks.
- Dynamic Application Security Testing (DAST): Simulates real-world cyberattacks on running web applications and APIs to identify live exploit vectors.
- Application Security Posture Management (ASPM): Centralizes findings across SAST, DAST, SCA, and external telemetry into an executive risk dashboard.
- Container Security: Identifies security flaws, misconfigurations, and outdated packages inside container base images and Dockerfiles.
- Interactive Developer Training: Interactive secure coding labs (Security Labs) and on-demand eLearning modules to upskill engineering teams.
- Penetration Testing as a Service (PTaaS): Combines automated scanning with expert human penetration testers for comprehensive compliance verification.
How much does Veracode cost?
Veracode operates on an enterprise subscription model tailored around scanned codebase size, application count, and modular product bundles.
Enterprise Licensing Model:
- Custom Enterprise Pricing: Billed annually based on the number of applications scanned, developer seats, and modular selections (SAST, DAST, SCA, Container Security, Veracode Fix).
- Tailored Packages: Custom configurations are available for mid-market engineering teams, large corporate enterprises, and government agencies requiring FedRAMP compliance.
- Free Demos & Proof of Concept: Prospective clients can schedule personalized demos and technical evaluation trials directly via veracode.com.
Disclaimer: Veracode is an enterprise B2B platform with customized pricing. Quotes are determined through personalized consultations and proof-of-concept evaluations at veracode.com.
Who should use Veracode?
Veracode is designed for enterprise engineering teams, regulated industries, and security leaders, including
- Financial Services & Banking: Meeting strict regulatory mandates (PCI DSS, SOX) with auditable security reporting and low false-positive rates.
- Healthcare & Life Sciences: Securing protected health information (PHI) and medical software in compliance with HIPAA and FDA guidelines.
- Public Sector & Government Agencies: Leveraging FedRAMP High security baselines to protect critical digital public infrastructure.
- DevSecOps & Cloud-Native Teams: Embedding security gates into automated CI/CD pipelines without slowing down continuous deployment cadences.
What are the best alternatives to Veracode?
Some of the strongest Veracode alternatives include
- Snyk
- Checkmarx
- GitHub Advanced Security
- Black Duck (formerly Synopsys Software Integrity Group)
- SonarQube / SonarCloud
- GitLab Ultimate (Security Dashboard)
What are the pros and cons of Veracode?
What are the pros of Veracode?
- Complete end-to-end coverage across SAST, DAST, SCA, container security, and cloud ASPM in a unified platform
- Veracode Fix actively writes remediated code patches, drastically cutting down developer security debt
- Demonstrated low false-positive rate (<1.1%) prevents alert fatigue and builds developer trust
- Enterprise governance and compliance reporting meet the most demanding regulatory audit standards
- Binary scanning capability enables analysis even when full source code access is restricted or unavailable
What are the cons of Veracode?
- Enterprise pricing is substantial, making it less accessible for early-stage startups and small indie teams
- Full platform onboarding and policy configuration across massive enterprise monorepos require dedicated administration
- DAST scanning setups for complex, multi-factor authenticated Single Page Applications (SPAs) can require fine-tuning
Why should you choose Veracode?
Many application security tools stop at listing hundreds of vulnerabilities, leaving overwhelmed developers with lengthy spreadsheets of alerts they have no time to fix. Veracode shifts the paradigm from detection to automated remediation. By pairing static, dynamic, and open-source scanning with AI-generated Veracode Fix patches and centralized ASPM governance, Veracode helps organizations eliminate security debt and ship secure code faster.
- Detect vulnerabilities across proprietary code, open-source libraries, containers, and live runtime environments
- Automate code remediation with AI-generated, reviewable patches via Veracode Fix
- Unify multi-vector application risk into an executive ASPM posture dashboard
- Satisfy rigorous global compliance frameworks with auditable, policy-driven reporting
How does Veracode compare to competitors?
The primary distinction between Veracode, Snyk, Checkmarx, and GitHub Advanced Security lies in testing breadth, binary analysis, and automated remediation. While Snyk is developer-centric for open-source dependencies and GitHub focuses on native repository alerts, Veracode provides an all-in-one platform covering SAST, DAST, SCA, container testing, and AI-driven automated remediation with proven enterprise scalability.
| Feature / Platform | Veracode | Snyk | Checkmarx | GitHub Advanced Security |
|---|---|---|---|---|
| Core Focus | Enterprise Application Risk Management & ASPM | Developer-First Open-Source & Cloud Security | Enterprise Code Security & AST | Native GitHub-Integrated DevSecOps |
| Testing Breadth | SAST, DAST, SCA, Containers & PTaaS | SAST, SCA, Containers & IaC | SAST, DAST, SCA, API & IaC | CodeQL (SAST), Secret Scanning & Dependabot |
| AI Remediation | Veracode Fix (AI code patches) | DeepCode AI / Automated PRs | Checkmarx AI Remediation | Copilot Autofix |
| Binary Analysis | Yes (Can scan compiled binaries) | No (Source code only) | Limited / Source-focused | No (Source code only) |
| Pricing Structure | Custom Enterprise Pricing | Free tier / Team & Enterprise plans | Custom Enterprise Pricing | Per-active-committer add-on license |
| Best For | Global enterprises needing unified ASPM, DAST, and compliance | Developer-led teams wanting fast open-source dependency fixes | Complex multi-language enterprise source analysis | Organizations standardized entirely on GitHub Enterprise |
How do we rate Veracode?
| Parameter | Rating (out of 5) |
|---|---|
| Vulnerability Detection & Accuracy | 4.9 |
| AI Remediation (Veracode Fix) | 4.8 |
| Testing Breadth (SAST, DAST, SCA) | 5.0 |
| Enterprise Compliance & Governance | 5.0 |
| Value for Enterprise Investment | 4.7 |
| Overall Score | 4.88 |
What is our review and verdict on Veracode?
Veracode remains a powerhouse in the application security and risk management sector. By uniting SAST, DAST, SCA, and container security into a cohesive ASPM platform with low false positives, Veracode provides unmatched visibility into corporate software risk. Its addition of Veracode Fix solves one of the biggest AppSec bottlenecks by automatically drafting verified remediation code, making it an invaluable asset for modern DevSecOps organizations.
Conclusion
Veracode makes application security more manageable by integrating testing directly into the development lifecycle. Instead of treating security as a last step, it helps teams identify and fix vulnerabilities early, reducing risk without slowing down releases. Its combination of automated scanning, actionable insights, and developer-friendly tools makes it practical for modern workflows. Overall, Veracode enables organizations to build secure software at scale while maintaining speed, compliance, and confidence in their code.
FAQ
What is Veracode and what does it actually do?
Veracode is a cloud-based application security platform that helps organizations identify, analyze, and fix vulnerabilities in their software throughout the development lifecycle. It provides a centralized system to scan code, monitor risks, and ensure secure software delivery across web, mobile, and cloud applications.
How is Veracode different from traditional security tools?
Traditional security tools often focus on isolated testing stages, but Veracode integrates security across the entire SDLC (software development lifecycle). It combines multiple testing methods—like static, dynamic, and open-source analysis—into one platform, giving teams unified visibility and faster remediation instead of fragmented workflows.
What features does Veracode offer for developers and security teams?
Veracode includes features such as Static Application Security Testing (SAST), Dynamic Application Security Testing (DAST), Software Composition Analysis (SCA), and AI-powered remediation through tools like Veracode Fix. It also offers risk dashboards, supply chain security, container scanning, and integrations with IDEs and CI/CD pipelines for continuous security.
How does Veracode use AI to improve security?
Veracode uses AI to prioritize vulnerabilities, analyze root causes, and generate automated fixes for security flaws. Its AI-driven remediation can suggest or apply patches quickly, reducing the time developers spend on manual debugging and helping teams resolve risks much faster.
Can Veracode scan open-source and third-party code?
Yes, Veracode includes Software Composition Analysis (SCA) to detect vulnerabilities in open-source libraries and third-party dependencies. It provides real-time insights, identifies hidden risks, and helps teams manage compliance and licensing issues within their software supply chain.
Who should use Veracode?
Veracode is designed for enterprises, fintech companies, SaaS businesses, and development teams that need strong application security. It’s especially valuable for organizations building complex applications or operating in regulated industries where security, compliance, and risk management are critical.
User Reviews
No reviews yet for Veracode.
Featured Tools
Featured AI tools from TechShark
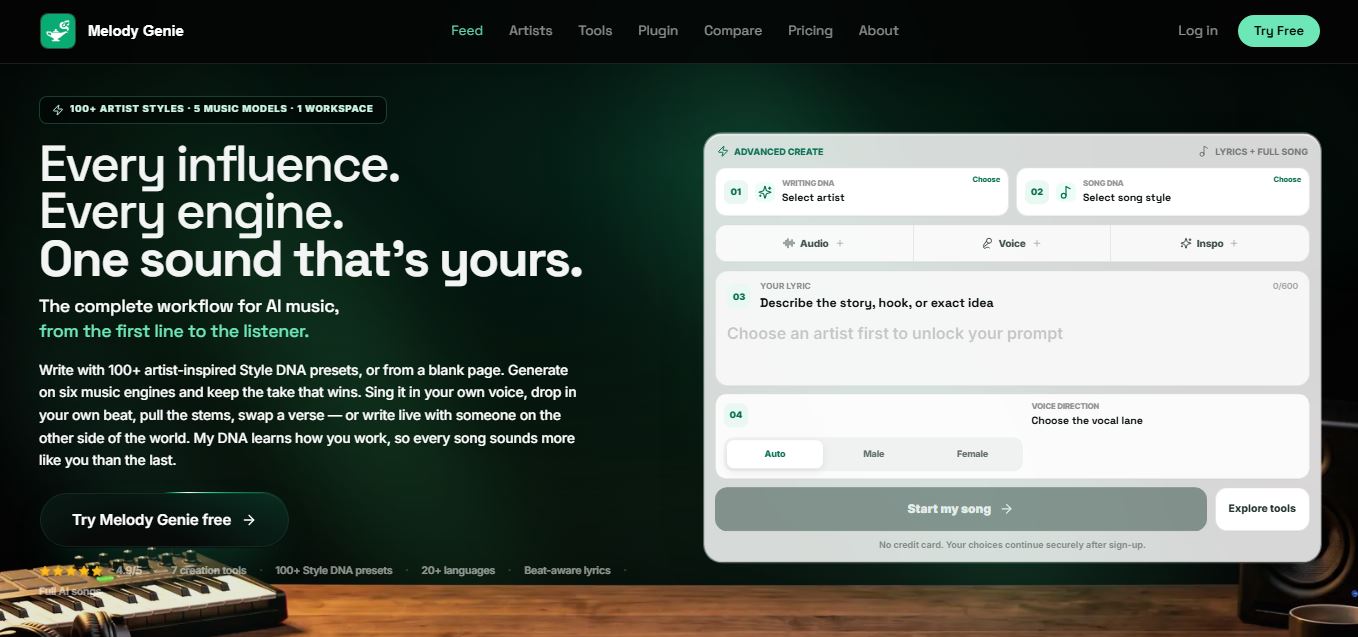
Melody Genie
MelodyGenie is an AI-powered music generator that creates original songs from simple text prompts. Users can choose styles, moods, and genres, then instantly generate melodies and full tracks, making it easy for creators, marketers, and hobbyists to produce custom music without musical expertise.
Freemium
Kimi AI
Kimi AI is an advanced AI assistant developed by Moonshot AI that helps you chat, research, write, code, and automate tasks in one place. It supports web search, file analysis, and multimodal inputs, and can even run autonomous “agent” workflows to complete complex tasks end-to-end.
Freemium
Fashion Diffusion AI
Fashion Diffusion is an AI-powered fashion design platform that helps brands and designers create clothing designs, virtual try-ons, AI models, product photos, and marketing visuals faster and cost-effectively.
Paid
Veo 4
Veo 4 AI is an AI video creation platform that generates dramatic videos from text, images, audio, and video prompts using realistic motion and synchronized sound.
Paid
Alternatives
Alternatives to Veracode
The best Veracode alternatives include Snyk, Checkmarx, GitHub Advanced Security, Black Duck, and SonarQube. While Veracode delivers an all-in-one Application Risk Management platform covering SAST, DAST, SCA, container scanning, and automated AI code fixes with Veracode Fix under low false-positive rates, alternatives like Snyk focus heavily on developer-friendly open-source fixes and GitHub Advanced Security integrates natively into GitHub Enterprise repositories.
 4.8
Varonis Systems
Cybersecurity
Varonis is a data security platform built to help organizations protect sensitive information across cloud, SaaS, and on-premises environments. It discovers and classifies data, analyzes permissions and activity, detects threats, and automates remediation. Security teams can use Varonis to reduce data exposure, strengthen compliance, investigate incidents, and improve security posture.
 4.9
GitGuardian
Cybersecurity
GitGuardian is an AI-powered code security platform that helps developers and security teams detect, prevent, and fix exposed secrets like API keys and credentials across code, CI/CD, and collaboration tools. It provides real-time alerts, automated remediation, and full visibility to reduce breach risks
 4.9
Vectra AI
Cybersecurity
Vectra AI is an AI-powered cybersecurity platform that helps businesses detect, investigate, and stop attacks across network, identity, and cloud environments. It uses behavioral analytics to identify real attacker activity, reduce alert noise, and provide clear, real-time insights so security teams can respond faster and prevent breaches.
 4.9
Darktrace
Cybersecurity
Darktrace is an AI-powered cybersecurity platform that helps businesses detect, investigate, and respond to cyber threats in real time. It uses self-learning AI to understand normal behavior across networks, cloud, and users, identifying anomalies and stopping advanced attacks before they cause damage.
 4.9
Cisco
Cybersecurity
Cisco is a global networking and cybersecurity platform that helps businesses connect, secure, and manage applications, users, and data across cloud and on-prem environments. It combines networking, security, and observability solutions to deliver reliable infrastructure, improve performance, and protect modern digital operations at scale.
 4.9
IRONSCALES
Cybersecurity
IRONSCALES is an AI-powered email security platform that helps businesses detect, prevent, and respond to phishing, business email compromise, and account takeover attacks. It combines adaptive AI with human insights to automatically analyze, remediate threats, and protect inboxes in real time across Microsoft 365 and Google Workspace.
 4.9
Abnormal Security
Cybersecurity
Abnormal AI is an AI-powered behavioral cybersecurity platform that helps businesses detect and stop advanced threats like phishing, account takeovers, and social engineering. It learns normal user behavior across email, identity, and cloud systems, then automatically identifies anomalies and responds in real time to prevent attacks.
 4.9
Proofpoint
Cybersecurity
Proofpoint is an AI-powered cybersecurity and compliance platform that helps businesses protect people, data, and communications from threats like phishing, email attacks, and data breaches. It uses advanced threat intelligence and automation to detect risks, prevent data loss, and secure interactions across email, cloud, and collaboration tools.
 4.9
Zscaler
Cybersecurity
Zscaler is an AI-powered cloud security platform that uses zero trust architecture to protect users, applications, and data across the internet and cloud. It replaces traditional VPNs and firewalls, enabling secure access, real-time threat protection, and simplified security operations for modern, distributed businesses.